Open Source / GitHub: How to secure API keys in env

Featured illustration for Open Source / GitHub: How to secure API keys in env

Open Source / GitHub: How to secure API keys in env. Actionable guide on how to secure API keys in env in context of android sms gateway open source. Include prerequisites, steps, limits, and internal links. Priced by devices and SMS send volume; BYO phone and operator credit.

Written by the SMS Gateway team for operators who run phones and airtime themselves — not for theoretical cloud SMS demos.

InformationAndroid SMS GatewayHow-ToHub E
Article
Published
June 27, 2026
Updated
July 6, 2026
Reading time
16 minute read

Key Takeaways

  • Secure API keys in env for Android SMS gateway projects: never commit Bearer tokens; load them at process start from a secret store.
  • Open GitHub samples should use placeholders — real keys belong in CI secrets or a vault.
  • Priced by devices and SMS send volume. You use your own phone and operator SMS credit. A leaked key can spend your plan volume and operator airtime.
  • Free 300 SMS lifetime is not a sandbox for public gists with live keys.
  • Rotate on staff change and on any paste into chat/MCP.
  • Developer Center shows how to create keys — this page is hygiene.

How to secure API keys in env when your GitHub repo talks to an Android SMS gateway: treat the Bearer token like a password that can send SMS on your SIM. Related: core secure-keys how-to. MCP auth. OWASP hard-coded secrets.

Priced by devices and SMS send volume. You use your own phone and operator SMS credit.

A README that says export SMS_GATEWAY_API_KEY=sk_live_… is a billable incident, not a quick start.

Env files and secret stores

Local: .env gitignored. Prod: platform secrets. Create/rotate keys in the control plane; confirm usage patterns in Developer Center.

Where keys leak

SurfaceRiskMitigation
Git commit / gistPublic scrapegitignore + secret scanning
CI logsEchoed envMasked variables
MCP / chatTranscript retentionTool loads env; never paste
Client appsExtractableServer-side only

Rotation and least privilege

Separate keys per environment and workload (OTP vs bulk). Revoke on offboarding. Pair with GDPR-minded handling.

CI and open-source repos

Example workflows inject secrets; sample code uses process.env.SMS_GATEWAY_API_KEY. Add .env.example with empty values only.

Runtime vs agent prompts

MCP wrappers and n8n credentials must read secrets from the host — not from the LLM context. See MCP auth concepts.

Related reading

Node.js API guide. Security.

Checklist

  • .env gitignored; example file empty.
  • Secret scanning on.
  • Prod keys in vault/platform.
  • No keys in mobile clients.
  • Rotation runbook exists.
  • Volume anomaly alerts considered.

Next steps

Rotate any demo keys, then operate within devices + SMS volume on your own Android and carrier credit.

Jump to the live product docs for this topic—not another long-form article.

FAQ

Frequently asked questions

Direct answers about android sms gateway open source how to secure api keys in env.

Is .env enough for production?

Fine for local. Production should use a secret manager or platform env injection, locked-down hosts, and no world-readable files.

Can I put the key in an MCP or n8n workflow screenshot?

No. Use credential stores. Treat chat transcripts as public.

What if a key leaked in a commit?

Revoke/rotate immediately in the panel, purge history if possible, and audit recent send volume.
Keep learning

Topically related guides—chosen by subject overlap, not a fixed sitewide footer.

Practical
android sms gateway open source checklist

API production readiness Checklist for Open Source / GitHub

API production readiness Checklist for Open Source / GitHub. Printable-style API production readiness checklist mapped to android sms gateway open source. Each item includes why it matters and a verification step. Priced by devices and SMS send volume; BYO phone and operator credit.

Jan 9, 202516 min
Read article
Information
android sms gateway open source how to avoid spammy wording

Open Source / GitHub: How to avoid spammy wording

Open Source / GitHub: How to avoid spammy wording. Actionable guide on how to avoid spammy wording in context of android sms gateway open source. Include prerequisites, steps, limits, and internal links. Priced by devices and SMS send volume; BYO phone and operator credit.

Jun 11, 202516 min
Read article
Information
android sms gateway open source how to choose prepaid vs postpaid sims

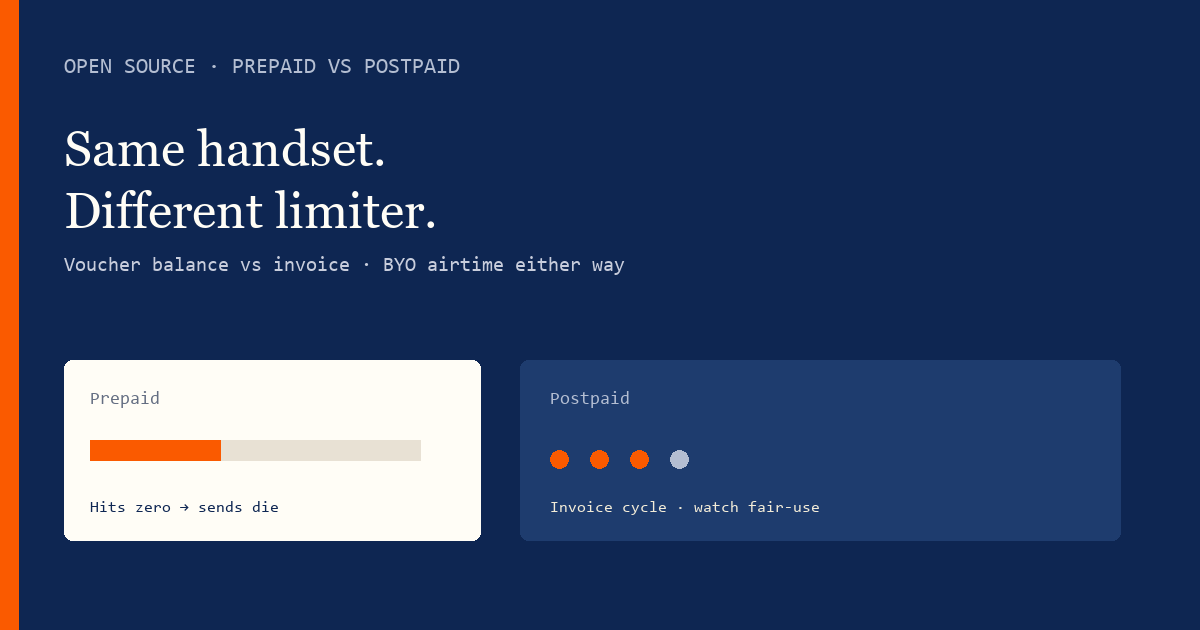
Open Source / GitHub: How to choose prepaid vs postpaid SIMs

Open Source / GitHub: How to choose prepaid vs postpaid SIMs. Actionable guide on how to choose prepaid vs postpaid SIMs in context of android sms gateway open source. Include prerequisites, steps, limits, and internal links. Priced by devices and SMS send volume; BYO phone and operator credit.

Feb 17, 202616 min
Read article

Browse the full Android SMS gateway knowledge base or return to how an Android SMS gateway works.

Get started

Test the gateway on your own Android phone

Install the app, pair one device, and validate your API flow before choosing a paid plan.

You supply the phone, SIM, and operator SMS credit.