Key Takeaways
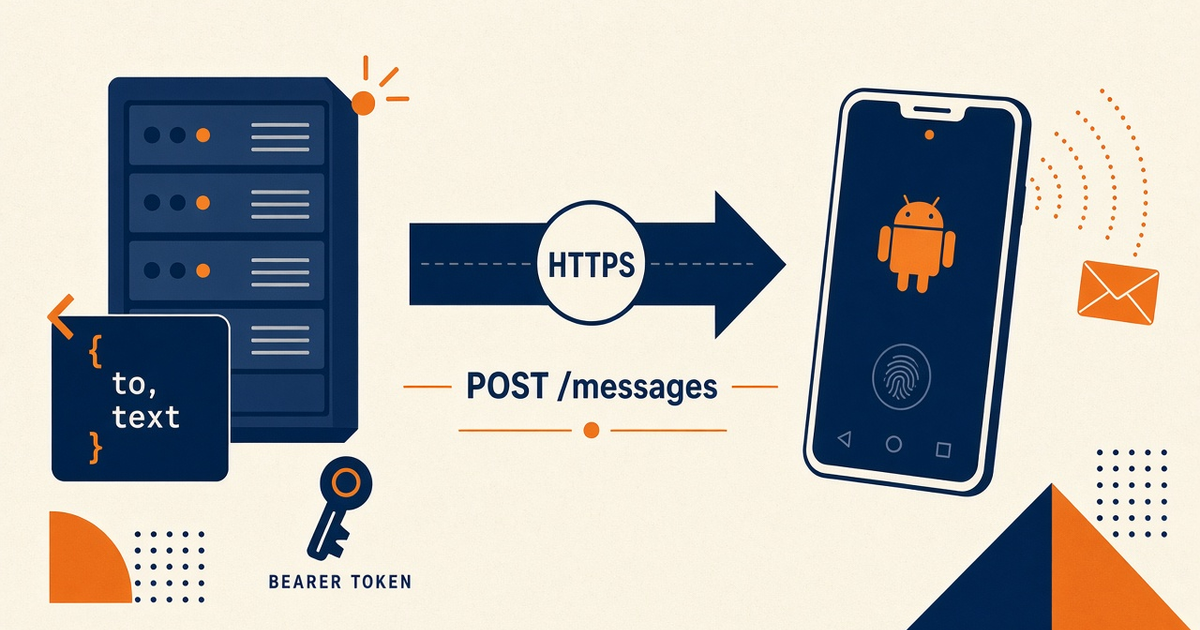
- mcp server mcp auth and api keys concepts: MCP talks to the agent host; REST Bearer talks to POST /messages. Do not mix those secrets.
- We do not ship a first-party Cursor or Claude plugin. You wrap HTTPS JSON.
- Put the gateway key on the MCP process env or vault — never in chat, git, or tool arguments.
- Dedicated keys per environment and per lane (canary vs marketing). OTP stays on the product path.
- Priced by devices and SMS send volume. You use your own phone and operator SMS credit. A leaked key still spends your operator airtime.
- Free is 300 SMS lifetime on one device — enough to notice a stolen canary.
Two auth planes, one radio
Search intent for mcp server mcp auth and api keys concepts is which credential does what. Service pricing is based on device count and total SMS sent through the gateway. MCP does not authenticate to the carrier. Your process still POSTs documented HTTPS JSON; the paired Android transmits. Spec: modelcontextprotocol.io.
If the model can print the Bearer, the key is already in the wrong plane. Rotate it. Treat chat logs as hostile storage.
Where the Bearer may live
Same discipline as API keys in env. The MCP wrapper is just another process that must not dump Authorization headers into traces. OWASP on hardcoded secrets.
| Plane | Allowed secret | Never |
|---|---|---|
| Agent host | MCP registration (command, args) | The SMS Gateway Bearer in the composer |
| MCP process | SMS_GATEWAY_API_KEY in env/vault | Tool JSON the model can echo |
| REST control plane | Authorization: Bearer on POST /messages | Query-string keys or invented OAuth tiles |
| Handset | Pairing to the account | A copy of the cloud API key on the SIM |
Not a Cursor or Claude plugin SKU
We do not list a first-party extension. You register a server you run. Cursor MCP concepts and Claude Desktop concepts cover host files. Do not copy keys between them.
Rotate without leaking traces
Issue a new key in the dashboard, update the MCP process env, restart the server, then revoke the old key. Do not paste the new value into a prompt “just to test.” Tool logs should store message ids, not Authorization headers. Walkthrough: MCP auth setup walkthrough.
Priced by devices and SMS send volume. You use your own phone and operator SMS credit. A loop that retries with a stolen key still burns airtime on your SIM.
OTP keys stay off agents
Customer login codes are a product path. Agents must not mint or display digits. Agentic OTP concepts. Use a dedicated, least-privilege key if ops canaries are allowed at all — never the production OTP lane. NIST SP 800-63 is the identity bar; chat transcripts are not an authenticator store.
Where the how-to lives
This page is the mental model. Field placement and rotation steps: MCP auth in-depth. Hardening: MCP auth security. Overview: SMS MCP server overview.
MCP auth concepts checklist
- REST Bearer on the process, not in the chat.
- No first-party plugin expectation.
- Separate keys for staging, canary, and marketing.
- OTP off the agent; digits never in traces.
- Rotate, restart, revoke — in that order.
Next steps
Put one canary key in env and send a staff number. Setup. Pricing. Downloads.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Android SMS gateway product guideDefinition, product, and how to buy
- download the Android gateway appGet the APK