Key Takeaways
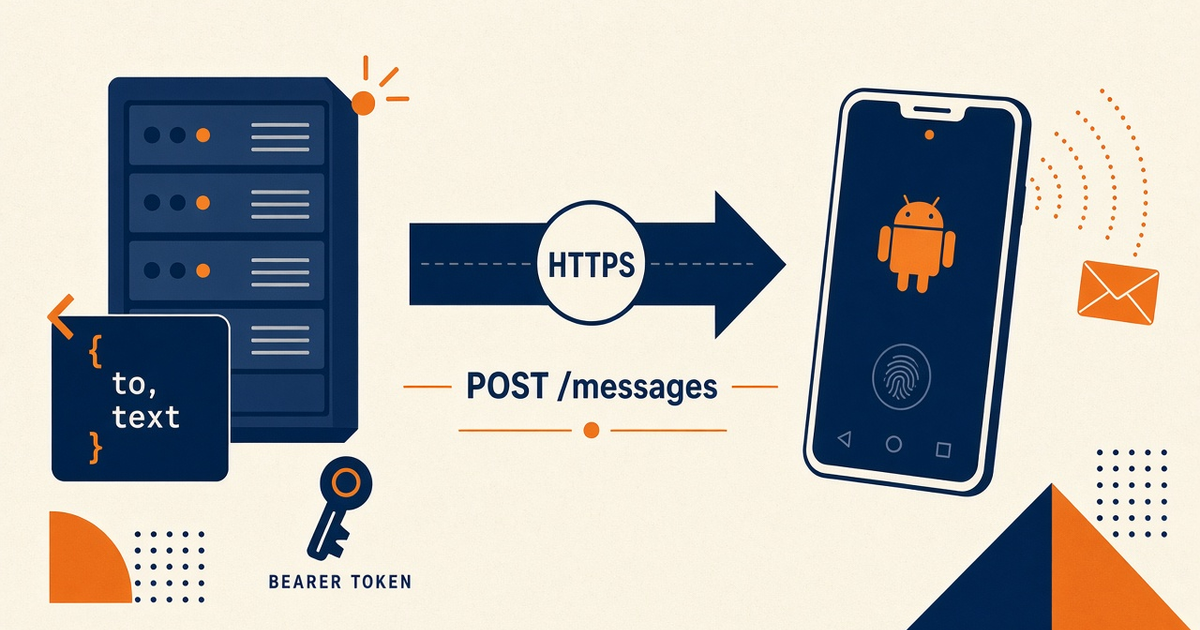
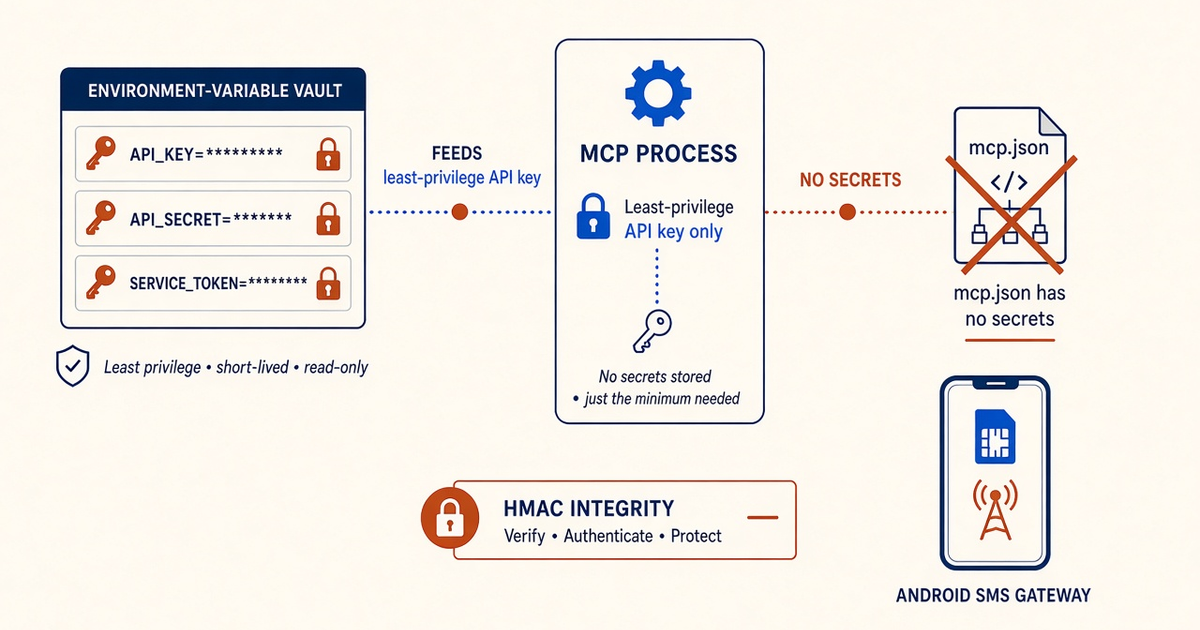
- MCP auth for an Android SMS gateway is least-privilege keys in process env — not a first-party plugin and not a token in mcp.json.
- Staging and production keys never share a host.
- HMAC protects inbound webhooks. It does not replace Bearer hygiene on outbound REST.
- Concepts sibling covers vocabulary; this page is the threat model.
- Developer Center owns live REST fields.
- BYO Android and operator credit. We meter devices and volume (Free 300 lifetime; paid from $19/mo).
Summary
MCP auth and API keys for an Android SMS gateway are about blast radius: one process, one env var, one scoped key. Concepts: auth concepts. Adapter: SMS MCP server overview. REST: Developer Center. Spec: modelcontextprotocol.io.
A production key on a laptop MCP host is not convenience. It is an unattended send desk with a chat box.
Env is the vault
Cursor and Claude Desktop register a command. They must not store the Bearer token. Pairing the Android is still setup. No first-party plugin.
Context
Teams paste keys into mcp.json because the tools “appeared.” That file is often committed. Treat the MCP process like any other REST client: API hub.
How to scope keys
- Issue a staging key for agent hosts; production keys stay on product servers.
- Least privilege: prefer read/list plus a canary send allowlist — not open send.
- One key per environment and per contractor workspace.
- Rotate when people leave or a chat dump might have included the token.
- HMAC secrets are separate from the API key; store both in env.
Where secrets must not live
| Location | Allowed | Why |
|---|---|---|
| Process env | API key + HMAC secret | Rotatable, not in git |
| mcp.json | Command / args only | Often committed |
| Agent chat | Never | Transcripts persist |
| Tool default args | Never the Bearer | Shows up in traces |
A leaked key spends airtime
Accepted sends meter platform volume and the operator. Devices and volume. Cap daily send on keys used by agents.
Rotation
Document who can mint keys. After rotation, restart the MCP process and confirm tools still authenticate. Last-seen on the phone is unrelated — a valid key with a sleeping OEM is still a radio outage.
HMAC is not a substitute
Verify inbound webhook signatures on the raw body. Webhooks. HMAC does not make a leaked outbound key safe.
Decision guide
Keep agent hosts on staging keys until allowlists exist. Production OTP stays on the product path — see agentic OTP security.
Checklist
- No token in git or mcp.json.
- Least-privilege key per env.
- HMAC secret separate.
- Rotation owner named.
- No first-party plugin claim.
Next steps
Audit what you log next: MCP logging and audit security.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Security and Trust CenterCompliance and posture
- Android SMS gateway product guideDefinition, product, and how to buy