Key Takeaways
- Agentic OTP over MCP is a least-privilege problem: the model must not hold send rights on a production SIM.
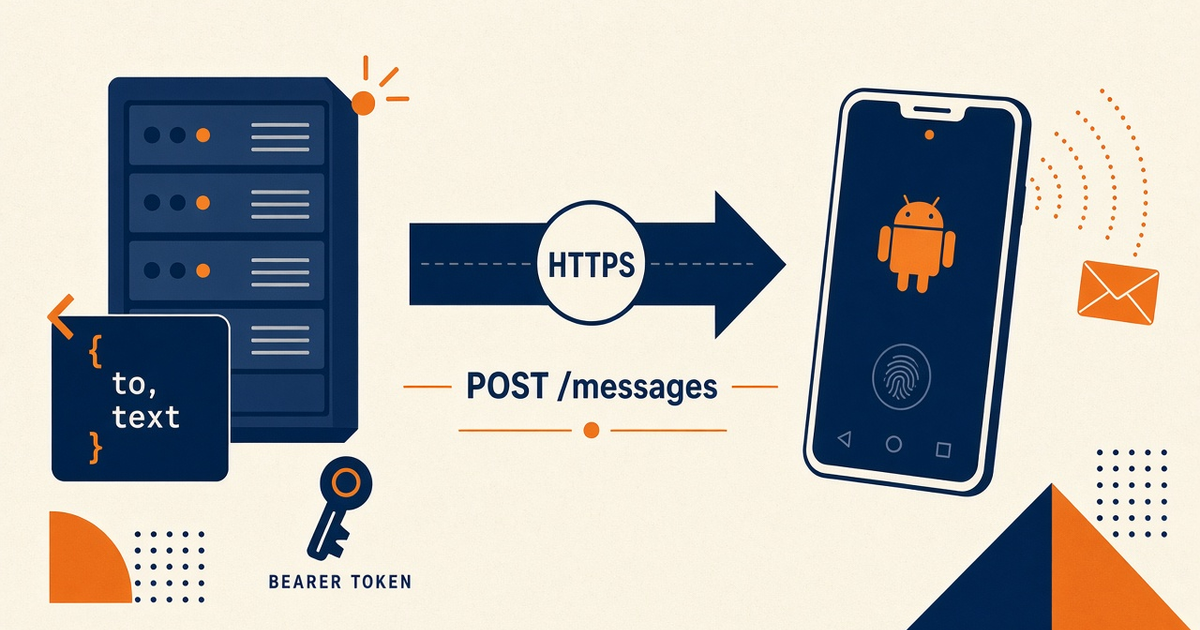
- No first-party MCP plugin. Your adapter wraps REST HTTPS/JSON.
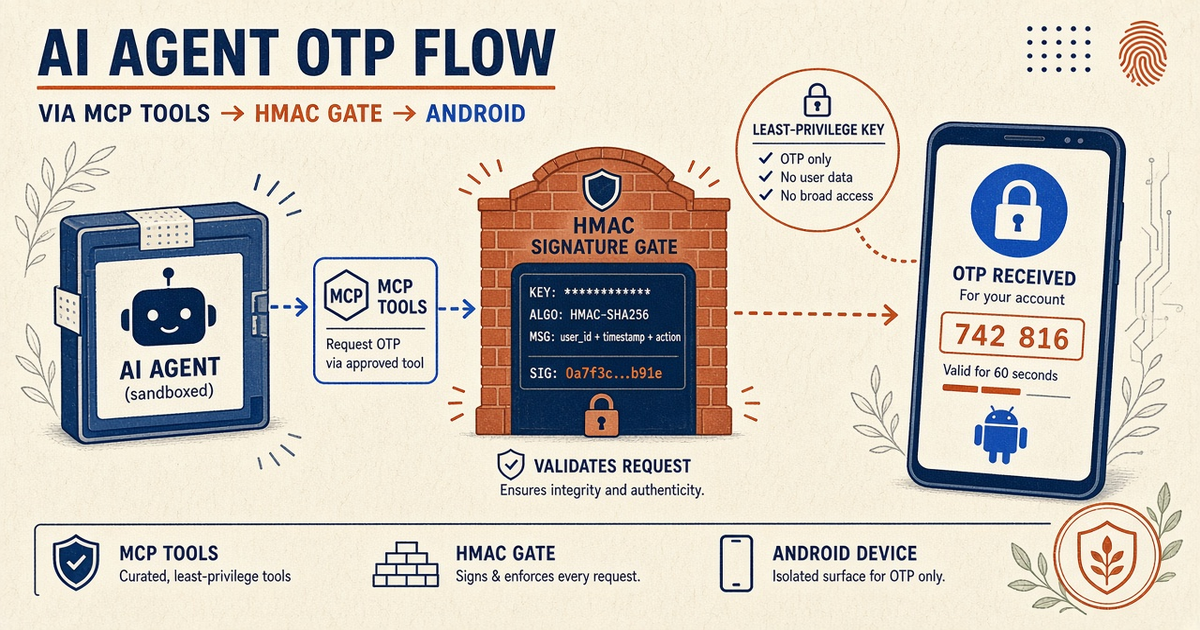
- HMAC-verify every webhook that can trigger a tool. Prompt injection is a send path.
- Keep OTP digits out of agent transcripts. Hash challenges in your app.
- Developer Center owns live fields.
- BYO Android and carrier credit. We meter devices and volume (Free 300 lifetime; paid from $19/mo).
Summary
Security for agentic OTP verification over MCP means treating the model as an untrusted operator of a send tool. Concepts: what is MCP for SMS. Adapter: SMS MCP server overview. Spec: modelcontextprotocol.io. Live REST: Developer Center.
An agent that can send OTP is a password-reset desk with no badge reader. Scope the tool like production IAM, not a demo.
The agent is a privileged client
MCP does not become an SMSC. Recipients still see your MSISDN. How the gateway works. Prompt injection can aim the tool at a new destination unless you allowlist.
Context
Teams want “the agent verifies the user.” The safe split: your app issues the challenge; the gateway sends the SMS; the agent never sees the digits. Tooling is an adapter, not a first-party plugin.
Security controls
- Least-privilege API key: staging vs production, OTP device only.
- Allowlisted destinations for any send tool the model can call.
- HMAC on webhooks; reject stale signatures.
- Idempotency keyed to the challenge id.
- Redact bodies in MCP logs and chat transcripts.
Control table
| Control | Why | Failure if skipped |
|---|---|---|
| Least-privilege key | Blast radius | Agent drains every SIM |
| HMAC inbound | Stop forged events | Public OTP trigger |
| Allowlist | Prompt injection | Codes to attacker MSISDN |
| No digits in context | Transcript leakage | OTP in logs forever |
OTP still spends airtime
Tool retries meter platform volume and operator SMS. Devices and volume. Cap agent send rate.
Operations
Last-seen alerts still belong on the phone. OEM sleep is not an MCP bug. Setup.
HMAC and inbound
If a webhook or tool waits for inbound SMS, verify signatures before the agent sees the event. Clock skew windows stay tight. See webhooks.
Decision guide
Ship agent-assisted OTP only when the product path owns verification and the MCP tool cannot enumerate customers. Delay if send_sms is unbounded.
Checklist
- No first-party plugin claim in runbooks.
- Env key only; rotated after contractor access.
- HMAC verified with raw body.
- OTP SIM isolated from marketing tools.
- Canary staff number only until ACL is proven.
Next steps
Compare host hardening in Claude Desktop SMS tools security and Cursor MCP SMS setup security.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- OTP and 2FA SMS on AndroidAuthentication flows
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Security and Trust CenterCompliance and posture