Key Takeaways
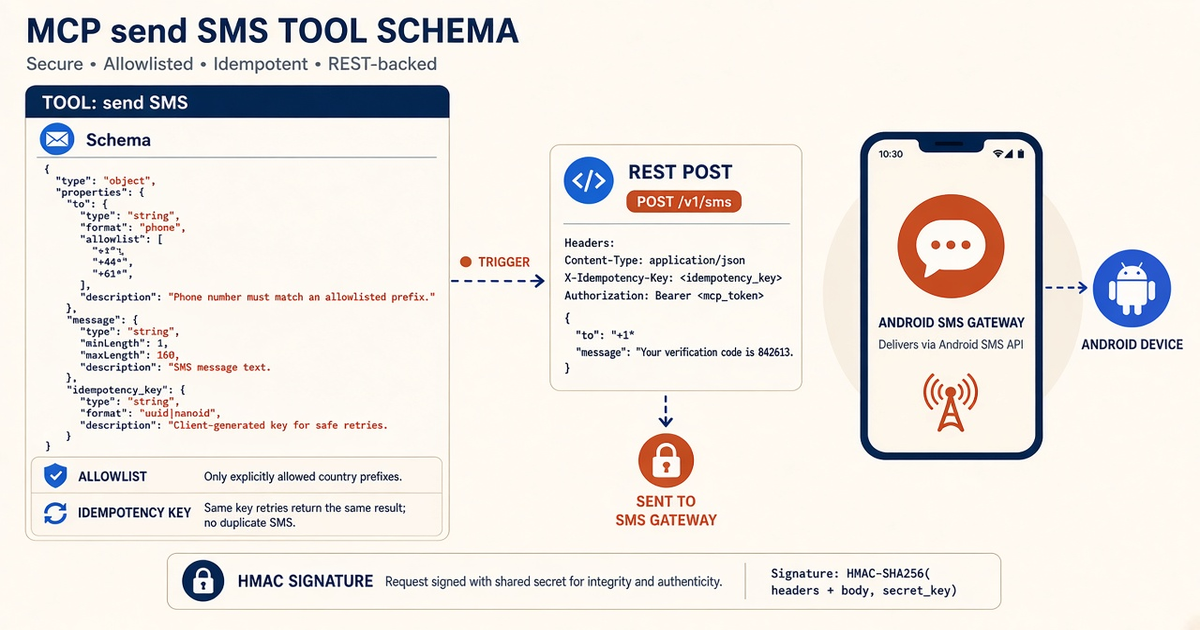
- send_sms MCP tool design is allowlist + idempotency + no free-form body echo — not a first-party plugin.
- Map arguments to Developer Center REST fields. Do not invent a second API.
- Least-privilege key in env. HMAC on any inbound that can trigger send.
- Return message ids. Never return OTP digits.
- BYO Android and operator credit. We meter devices and volume (Free 300 lifetime; paid from $19/mo).
Summary
Security for send_sms MCP tool design is the argument surface: what the model is allowed to fill. Concepts: send tool concepts. Catalog posture: securing SMS MCP tools. Spec: modelcontextprotocol.io. REST: Developer Center.
A tool that accepts body + to + from as free text is a programmable SIM. Design the schema like IAM, not like a demo.
The tool is a REST wrapper
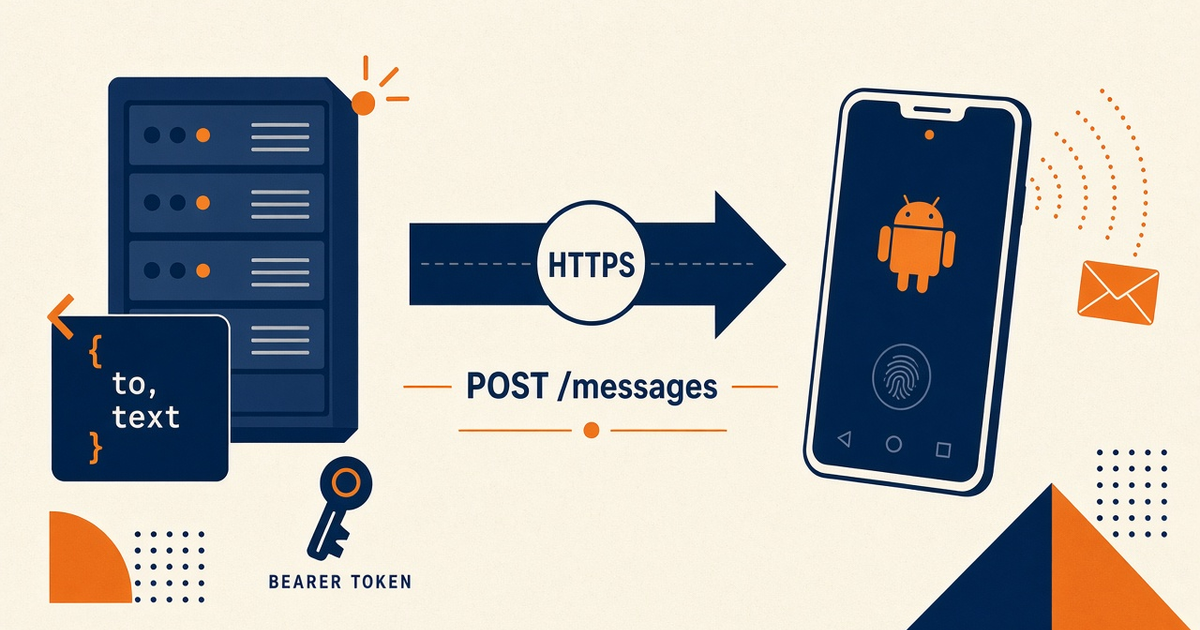
POST /messages (names from Developer Center). No first-party plugin. The Android still spends operator credit. How the gateway works.
Context
Agents will pass whatever the schema allows. Fail closed on missing idempotency. OTP templates belong in your app, not in tool args.
Design the send tool
- Split canary_send vs bulk_send. Keep bulk off agent hosts.
- Destination enum or server allowlist — not a raw MSISDN string for the model.
- Idempotency-Key from a business id the server validates.
- Return gateway message id; redact body in the result.
- Env Bearer; never in the tool description.
Argument table
| Arg | Safe shape | Unsafe shape |
|---|---|---|
| to | Allowlisted id | Any E.164 string |
| body | Template id | OTP digits from the model |
| idempotency | Required server-side | Optional “if you remember” |
| device | Fixed OTP pool | Agent picks any handset |
Each call can spend airtime
Accepted sends meter platform volume and the carrier. Devices and volume. Rate-limit in the adapter.
Operations
Last-seen on the phone is still uptime. Setup. Do not retry 4xx from the tool.
HMAC and idempotency
If a webhook can trigger send_sms, verify signatures on the raw body first. Webhooks.
Decision guide
Ship canary_send only until allowlists are proven. Customer OTP stays on product REST — see agentic OTP security.
Checklist
- Allowlist in the server.
- Idempotency required.
- Bodies not in results.
- Env key; HMAC inbound.
- No first-party plugin claim.
Next steps
Vocabulary: what is MCP for SMS (security).
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Security and Trust CenterCompliance and posture
- Android SMS gateway product guideDefinition, product, and how to buy