Key Takeaways
- API how-to: secure API keys in env. Bearer tokens belong in the process environment or a vault — not git, not the browser, not the APK.
- Hub C cornerstone is the Android SMS gateway API guide. Rotate keys when people leave.
- Server-side only. A React bundle with a key is a public sender.
- Staging and production keys must differ. Job payloads must not carry the secret.
- Priced by devices and SMS send volume. You use your own phone and operator SMS credit. A leak spends your SIM and your platform volume.
- PHP/C# pages are REST samples, not a packaged SDK.
Hub C: android sms gateway api how to secure api keys in env. You POST JSON with a Bearer token. That token is as powerful as the dashboard. Cornerstone: Android SMS gateway API. Sibling: app how-to on keys. Docs: Developer Center.
Priced by devices and SMS send volume. You use your own phone and operator SMS credit.
If the key is in the repo, it is already in last week’s CI cache, a fork, and a laptop that left the building.
Where the key must live
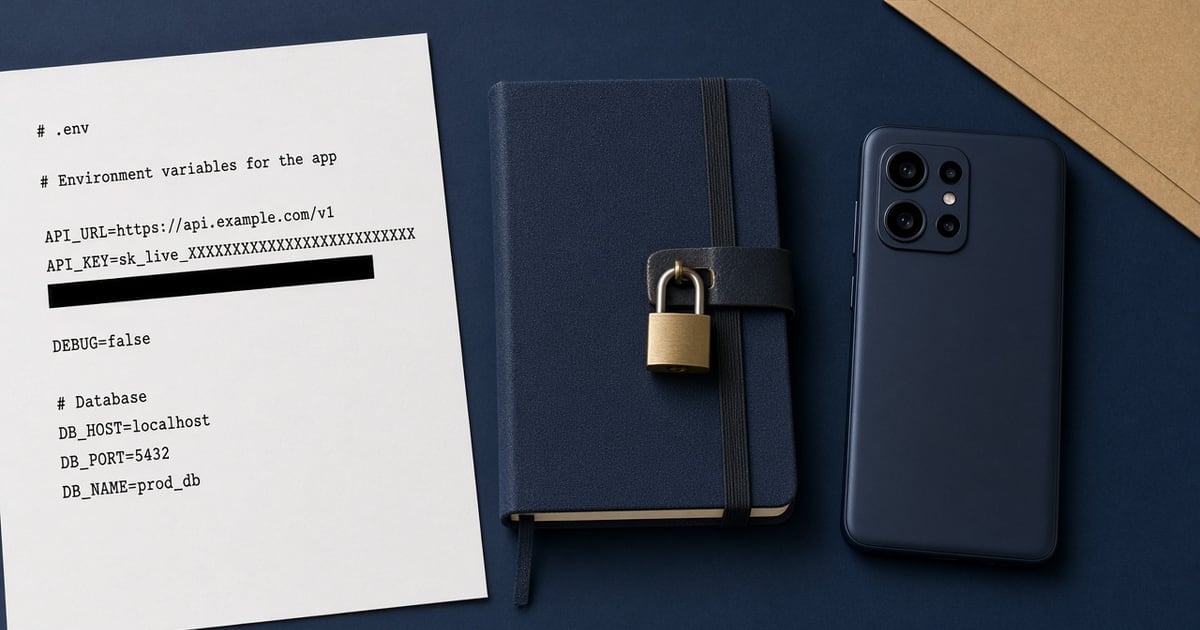
Process environment, then a vault (cloud secret manager, K8s secret, .NET user secrets for laptop only). Inject at runtime. Never bake into images as a layer you will push to a public registry “just this once.”
Places that leak
- Frontend bundles, mobile apps, Postman public workspaces.
- Screenshots in tickets, Slack, and README “quick starts.”
- Git history after you “removed it in the next commit.”
- Verbose access logs that print Authorization.
Background: OWASP hard-coded key notes.
Env table: local, CI, prod
| Stage | Acceptable | Not acceptable |
|---|---|---|
| Laptop | gitignored .env / user secrets | Key in appsettings.Development.json committed |
| CI | Masked secret store | echo $KEY in build logs |
| Production | Vault + IAM to the worker | Same key as staging forever |
| Workers (Hangfire etc.) | Env on the worker process | Key in the job payload |
ASP.NET workers: queue workers.
Rotation after people leave
Create a new key, deploy env, disable the old one. Do not wait for a “security quarter.” GDPR-minded logs: GDPR-minded API data.
Never in the Android binary
The handset is a radio. It should not hold your account token. Pairing uses the official app, not a key you compiled in.
Samples are not a secrets manager
PHP and C# pages are REST examples, not NuGet/Composer products and not “download PHP SDK.” Copy the HTTPS shape; do not copy a literal key from a gist.
A leaked key spends your airtime
Priced by devices and SMS send volume. You use your own phone and operator SMS credit. Platform volume and the SIM both move if someone else POSTs. Free 300 SMS lifetime can vanish to a scraper. Rotate; do not ask us to refund the operator.
Checklist
- Key only on the server.
- .gitignore includes .env and local secret files.
- CI secrets masked.
- Staging and prod keys differ.
- Rotation owner named.
- Authorization logs redacted.
- No key in APK or SPA.
- Developer Center for live auth scheme.
- Incident path: disable key, then post-mortem.
- No “unlimited SMS” assumption if the key leaks.
Next steps
Read the API hub, then security. Env is boring. Leaks are not.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Android SMS gateway product guideDefinition, product, and how to buy
- download the Android gateway appGet the APK