Key Takeaways
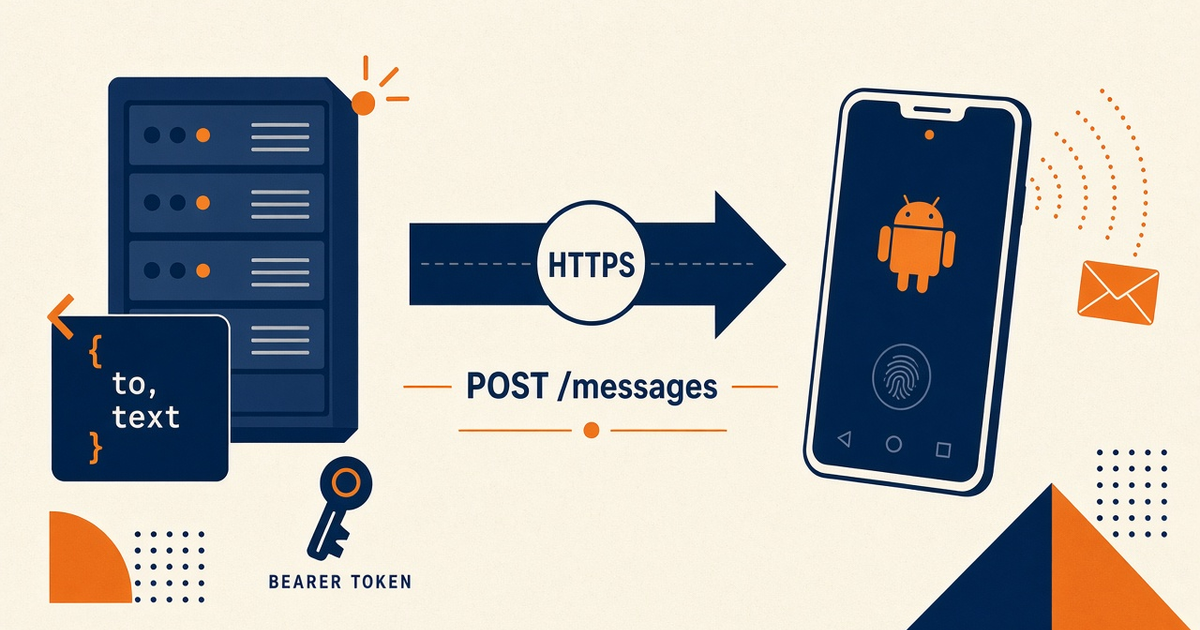
- android sms gateway server reverse proxy and HTTPS is hardening a panel you host — terminate TLS, do not log Bearer tokens.
- This is not an exploit guide. It is defensive TLS for operators maintaining their own edge.
- Webhooks you register must be HTTPS with signature checks. HTTP callbacks leak and fail audits.
- A reverse proxy does not send SMS. The Android SIM still does.
- Priced by devices and SMS send volume. You use your own phone and operator SMS credit. Paid from $19/month if you skip self-hosting.
- Start from the server cornerstone. Pair with the cloud-relay vs local spoke.
Why HTTPS sits in front of a local panel
Search intent for android sms gateway server reverse proxy and HTTPS is putting TLS in front of a control plane you host. Service pricing is based on device count and total SMS sent through the gateway. The proxy is not the modem. Start from the server cornerstone and cloud relay vs local.
If access logs print Authorization headers, you do not have a “verbose logging” preference. You have a credential dump.
OWASP TLS guidance is a useful floor (Transport Layer Protection Cheat Sheet). This page does not walk exploit or bypass steps.
TLS you actually need
Terminate TLS at the edge you control. Keep certificates current. Prefer modern TLS; disable leftover HTTP on the admin hostname once you are ready. Do not paste copy-paste “bypass” configs. Mozilla’s SSL configurator is a reference for operators (ssl-config.mozilla.org).
| Control | Why | Common miss |
|---|---|---|
| TLS 1.2+ at the edge | Keys and numbers in transit | Plain HTTP “on the LAN is fine” |
| HSTS when you mean it | Stop downgrade on admin laptops | HSTS on a name you still use HTTP for |
| No Authorization in access logs | Bearer tokens are passwords | Default verbose proxy logging |
| Webhook HTTPS + signatures | Forged DLR is an incident | http:// callback “just for staging” in prod |
What never belongs in logs
Strip or redact Authorization. Keys live in env on the worker — API keys in env. Do not put Bearer tokens in query strings. Hosted API contract: docs.sms-gateway.app.
Callbacks must be HTTPS too
Register HTTPS webhook URLs. Verify signatures. Idempotent handlers. HTTP “staging” URLs that leak into production are how DLR gets spoofed. SMS webhook integration.
Maintained path vs your proxy
If you use the hosted control plane, you do not need to invent an edge in front of api.sms-gateway.app (that host is not the API). Phones still need setup — device setup. Priced by devices and SMS send volume. You use your own phone and operator SMS credit. OTP: OTP verification.
HTTPS checklist
- TLS on the admin hostname; HTTP off when ready.
- Authorization not in logs.
- Webhook HTTPS + signatures.
- Cert expiry on the calendar.
- Phone + airtime still owned.
Next steps
If you self-host, put TLS on the edge and redact logs. If you do not want that job, use the maintained app from downloads. Pricing.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- device and SMS volume pricingPlans and allowances
- Android SMS gateway product guideDefinition, product, and how to buy
- SMS API documentationLive endpoint reference
- download the Android gateway appGet the APK