Key Takeaways
- Python OTP over an Android SMS gateway is httpx/requests HTTPS + Bearer env key — not a pip “Complete Python SDK.”
- Hash challenges at rest; cooldown per number; thin handlers; queue the send.
- Verify webhook HMAC on the raw body; never put keys in client apps.
- OEM + plan caps still apply; no Unlimited SMS titles.
- Developer Center owns live REST fields.
- BYO Android and operator credit. We meter devices and volume (Free 300 lifetime; paid from $19/mo).
Summary
Send OTP with Python through an Android SMS gateway API using REST — hash at rest, queue the send, verify in your app. Hub: Android SMS Gateway API. Docs: Developer Center. Use case: OTP verification. Pricing: devices + volume (Free 300 lifetime; paid from $19/mo) — pricing.
A pip package that claims to “remove Android SMS rate limits” is not a dependency. It is a compliance hazard with a setup.py.
REST, not an SDK
Use httpx/requests with Authorization: Bearer from environment variables. No official multi-language Python SDK from us. Confirm path and JSON fields in Developer Center.
# Conceptual — confirm URL/fields in Developer Center
import httpx, os
r = httpx.post(
    send_url,
    headers={"Authorization": f"Bearer {os.environ['SMS_GATEWAY_API_KEY']}"},
    json={"to": e164, "text": body, "client_ref": challenge_id},
    timeout=15.0,
)
Context
OTP and marketing must not share unbounded senders. Prefer GSM-7 friendly templates. Keep the handset online via setup.
OTP send design
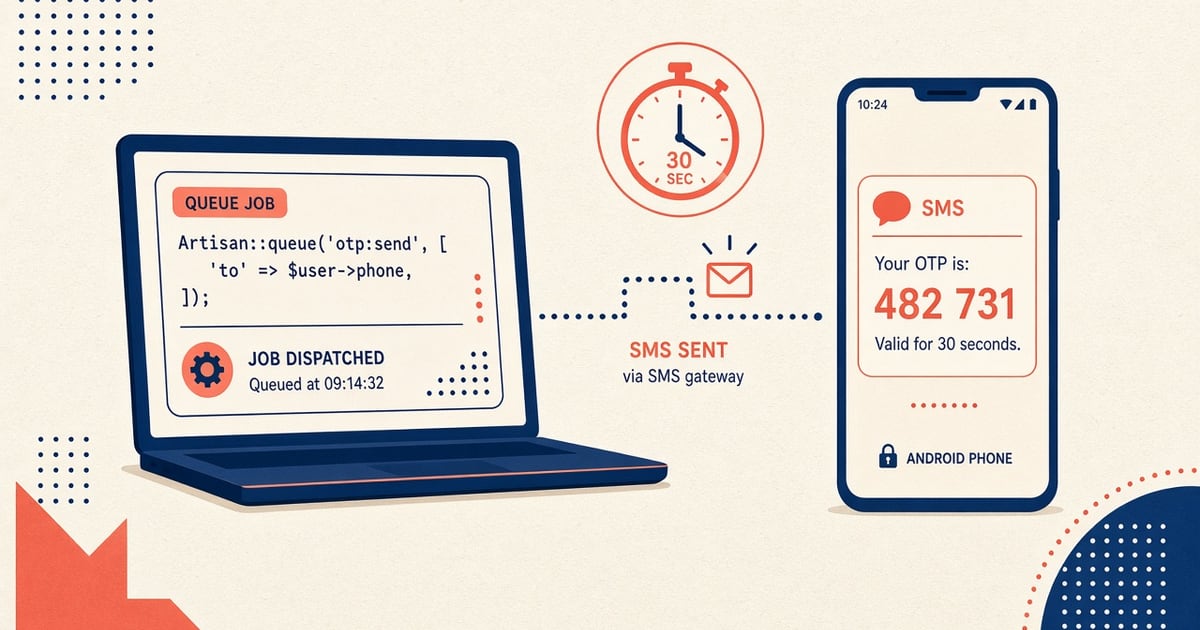
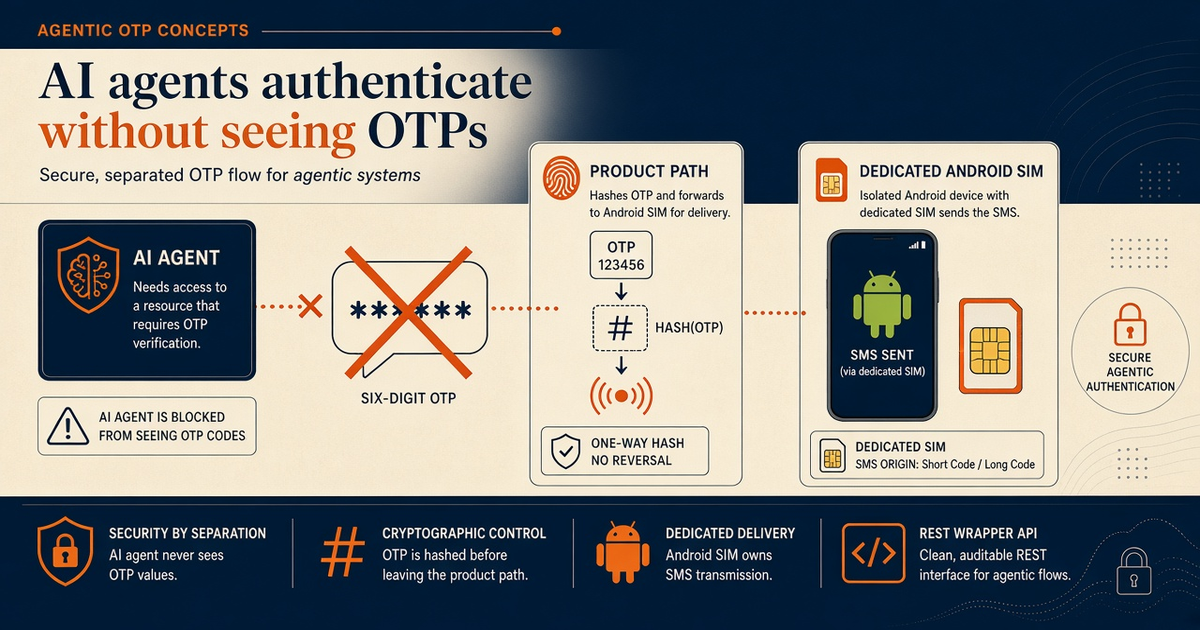
- Generate code server-side; store hash + TTL + attempts.
- Enqueue send with stable client_ref / idempotency key.
- Return cooldown UX; do not block on DLR.
- On submit, compare hash; invalidate.
- Controlled resend under per-number limits.
Layer table
| Layer | Owns | Must not |
|---|---|---|
| Python auth service | Hash, TTL, lockout | Log plaintext OTP |
| Worker | REST send + backoff | Retry 4xx forever |
| Gateway + Android | Queue, radio, DLR | Supply operator airtime |
| Webhook handler | HMAC + idempotent status | Trust unsigned POSTs |
Each code spends airtime
Accepted sends meter platform volume and the carrier. Free/Developer pause when allowance is exhausted. Raise OEM ceilings carefully — never title “Unlimited SMS.”
Operations
Alert on last-seen and Pending age. Canary with staging keys — CI must not empty production SIMs.
HMAC and least privilege
Verify webhook signatures over the raw body. Keep API keys server-side only.
Decision guide
Same physics as Node send OTP— different worker runtime.
Checklist
- REST httpx + env Bearer; no client keys.
- Hash + TTL + cooldown + idempotent resend.
- HMAC webhooks; timeouts on HTTP.
- OTP pool isolated.
- No SDK product claim; no Unlimited SMS titles.
Next steps
Competitor dual-SIM depth: RBSoft dual SIM guide.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- OTP and 2FA SMS on AndroidAuthentication flows
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Android SMS gateway product guideDefinition, product, and how to buy