Key Takeaways
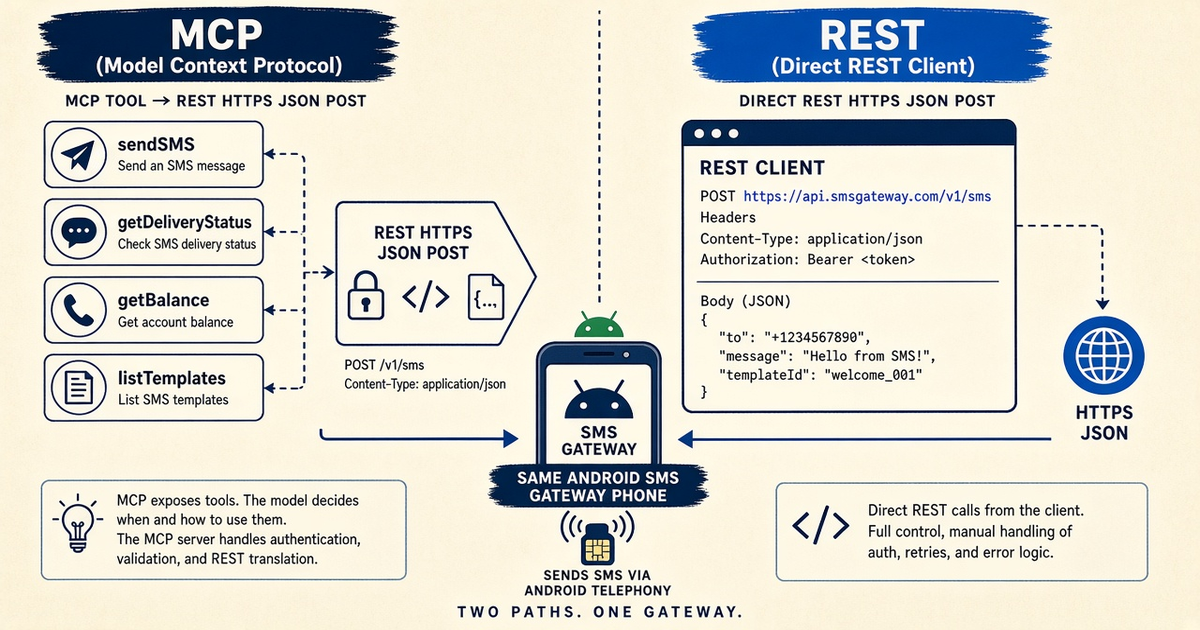
- MCP vs REST security is not two SMSCs. MCP is an adapter; REST HTTPS/JSON is the contract.
- No first-party MCP plugin. Tools must not invent fields missing from Developer Center.
- Agents expand prompt-injection and transcript leak surface. Product OTP should stay on REST.
- HMAC and least-privilege keys apply to both clients.
- BYO Android and operator credit. We meter devices and volume (Free 300 lifetime; paid from $19/mo).
Summary
MCP server vs REST API security: the radio does not care which client queued the job. Concepts: MCP vs REST concepts. Canonical send: Android SMS Gateway API. Spec: modelcontextprotocol.io. Live fields: Developer Center.
MCP does not harden REST. It wraps REST in a process that also talks to a model. Treat that as extra privilege, not extra safety.
REST stays canonical
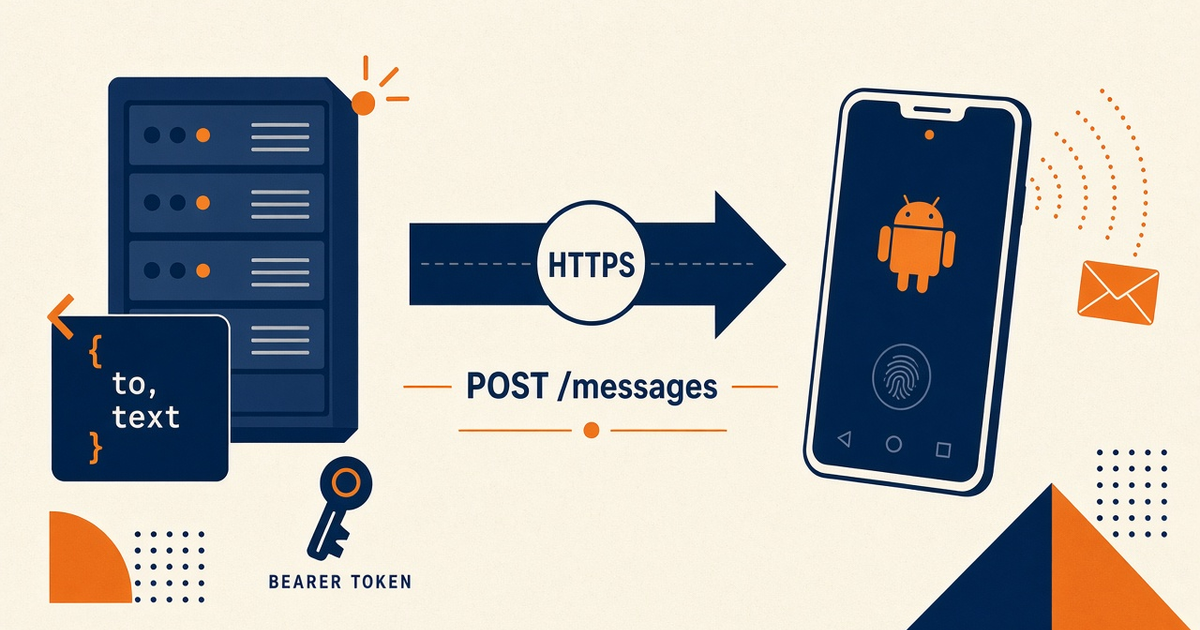
Tools map to POST /messages, DLR, optional inbound. Inventing fields is a bug. We do not ship a first-party MCP product that replaces Developer Center.
Context
Product OTP belongs on your backend REST client with hashed challenges. MCP is for ops, canaries, and internal agents — if allowlists exist. Setup still pairs the phone.
When MCP adds risk
- Prompt injection can aim a send tool.
- Transcripts retain arguments you forgot to redact.
- Desktop hosts mix file access with send rights.
- Schema drift duplicates a private, undocumented API.
Control comparison
| Control | REST app | MCP adapter |
|---|---|---|
| Env Bearer | Required | Required (not mcp.json) |
| HMAC inbound | Required | Required if tools ingest webhooks |
| Allowlist dest | App logic | Mandatory for model-callable send |
| OTP digits | Hashed in app | Must never enter tool args |
Same SIM, same bill
Either client spends operator airtime and platform volume. Devices and volume.
Operations
Last-seen and OEM killers are radio issues. Do not debug them as “MCP vs REST.”
HMAC on both paths
Verify signatures on the raw body before side effects. Webhooks.
Decision guide
Use REST for customer OTP. Use MCP for constrained ops. If the model can send to any MSISDN, unplug the key.
Checklist
- Tool schema matches Developer Center.
- Least-privilege key.
- HMAC on inbound.
- OTP not on the agent path.
- No first-party plugin claim.
Next steps
No-code comparison: MCP vs Zapier security.
Related product pages
Jump to the live product docs for this topic—not another long-form article.
- SMS API documentationLive endpoint reference
- device and SMS volume pricingPlans and allowances
- Twilio vs Android SMS gatewayCloud vs own-SIM cost model
- Security and Trust CenterCompliance and posture